

Trusted by 3,600+ verified brands
Cyber Resilience Act representation for connected products
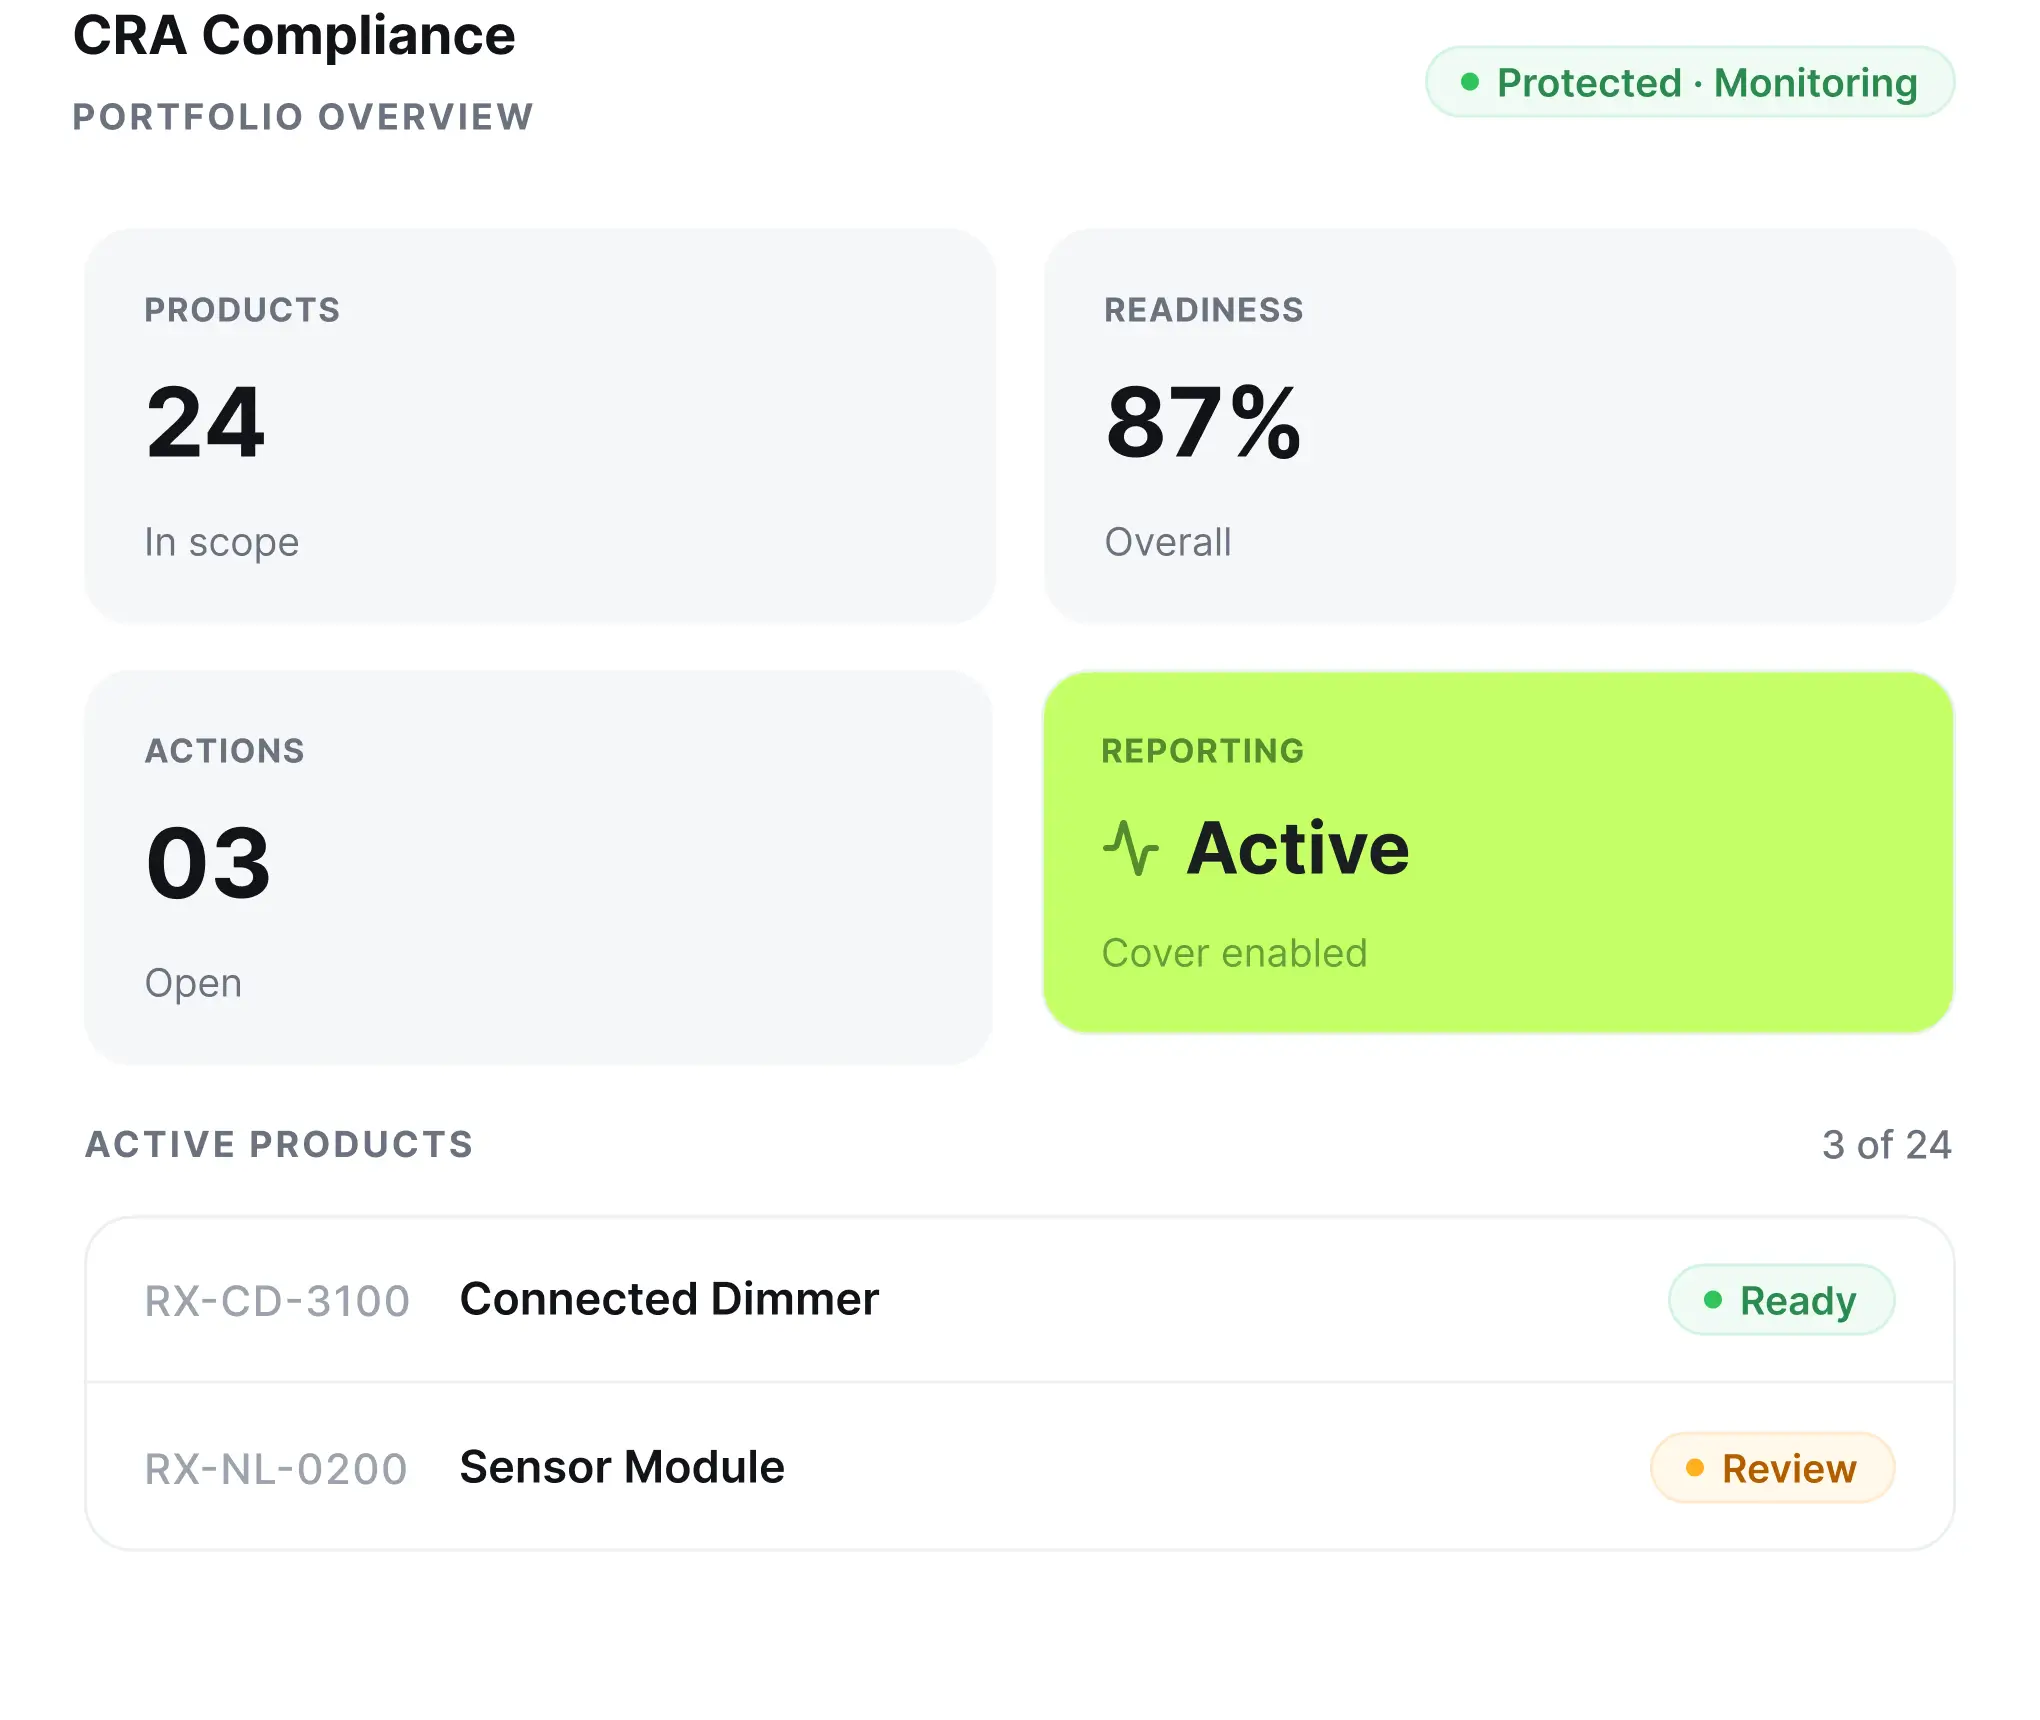
Reporting duties under Regulation (EU) 2024/2847 became live on 11 September 2026 — and they apply to products you are already selling, not just new ones. Euverify acts as your EU authorised representative, holds your file for the authorities, and handles your 24-hour notifications.
Trusted by Leading Brands


What is the Cyber Resilience Act?
From a connected product to a filed notification, in one place.
The CRA is the EU’s cybersecurity law for products with digital elements: anything with software or firmware that connects to a device or network. It sets security requirements and requires reporting actively exploited vulnerabilities or severe incidents to a national CSIRT and ENISA within 24 hours of discovery.
An EU authorised representative is optional under Article 18. It determines who holds your EU file, answers market surveillance authorities, and receives your reports. Without one, Article 14(7) sets the route by cascade: importer, then distributor, then wherever most users are — shifting as distribution changes, with a 24-hour clock running while you work it out.
Everything you need for CRA compliance
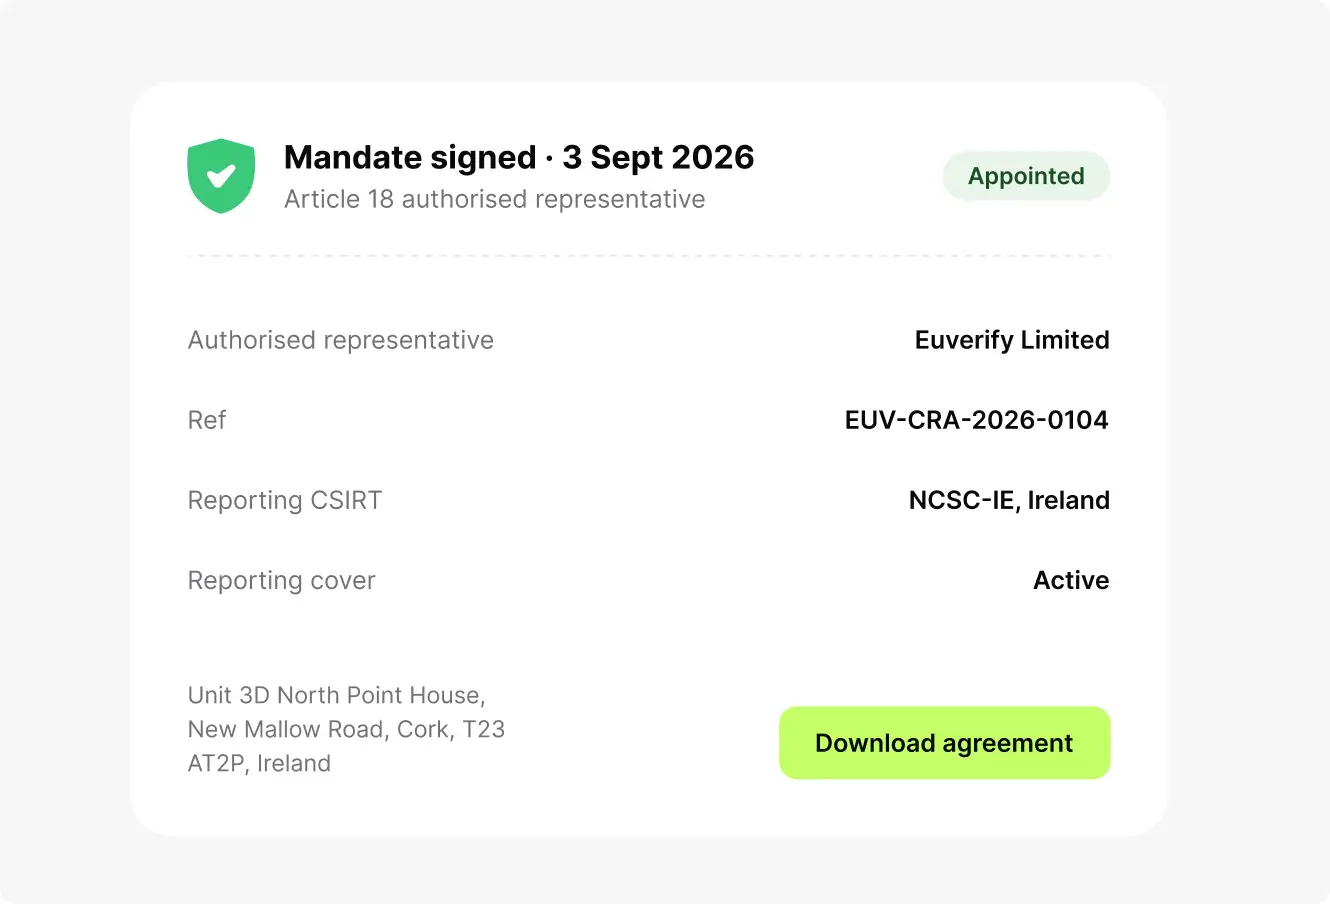
EU authorised representative, appointed in minutes
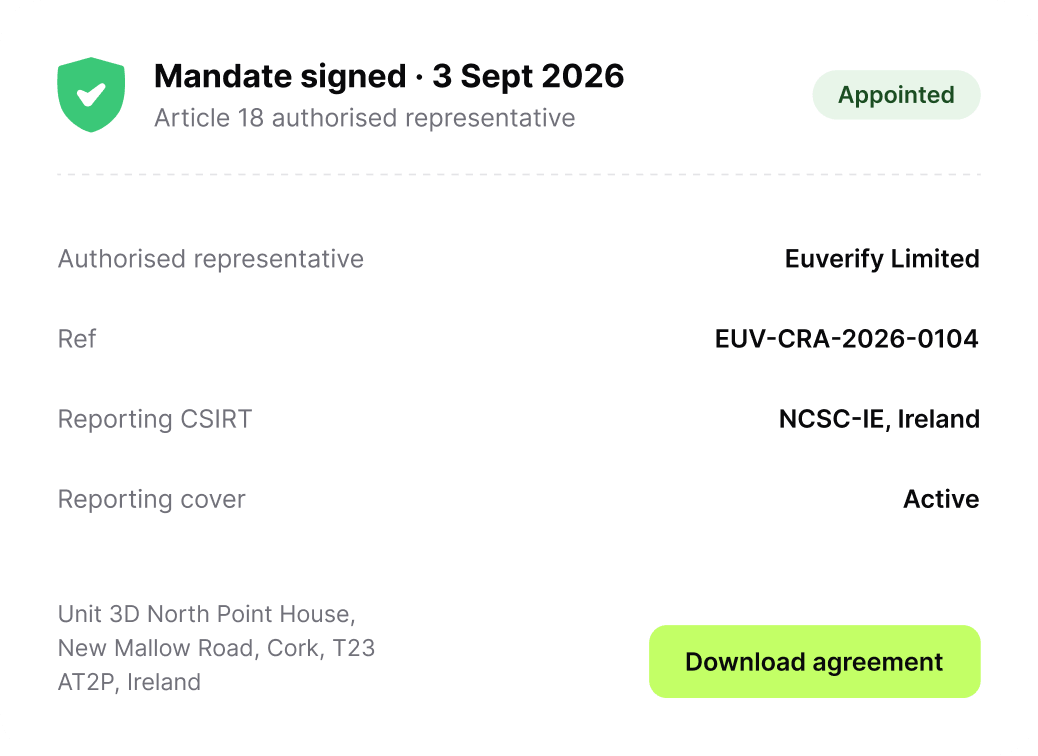
One signed mandate, active the same day
Euverify Limited in Cork is named as your authorised representative under Article 18. We hold your EU Declaration of Conformity and technical documentation at the disposal of market surveillance authorities for ten years after each product is placed on the market, or for the support period if longer. Our legal name and Irish address are yours to use on packaging, listings and documentation.
24-hour reporting, handled
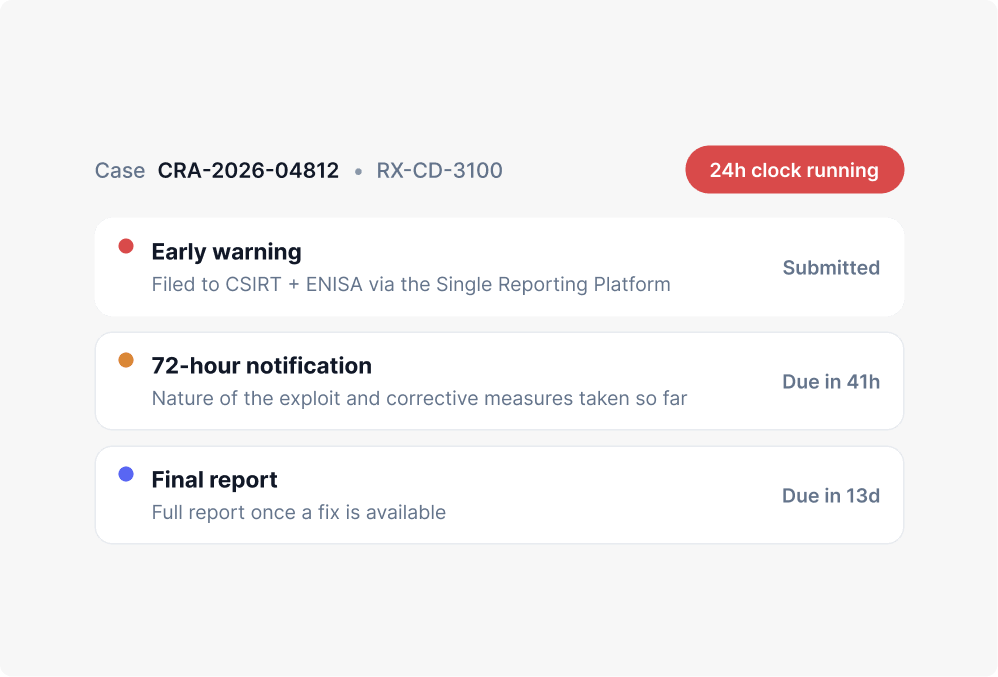
The clock starts when you find out, not when you finish investigating.
Tell us and we take it from there: we draft the early warning, submit it through the ENISA Single Reporting Platform on your instructions, and run the 72-hour notification and the final report from the same case. All three stages are tracked against the moment you became aware, and we help draft the notice to users that Article 14(8) requires.
We tell you which of your products are in scope
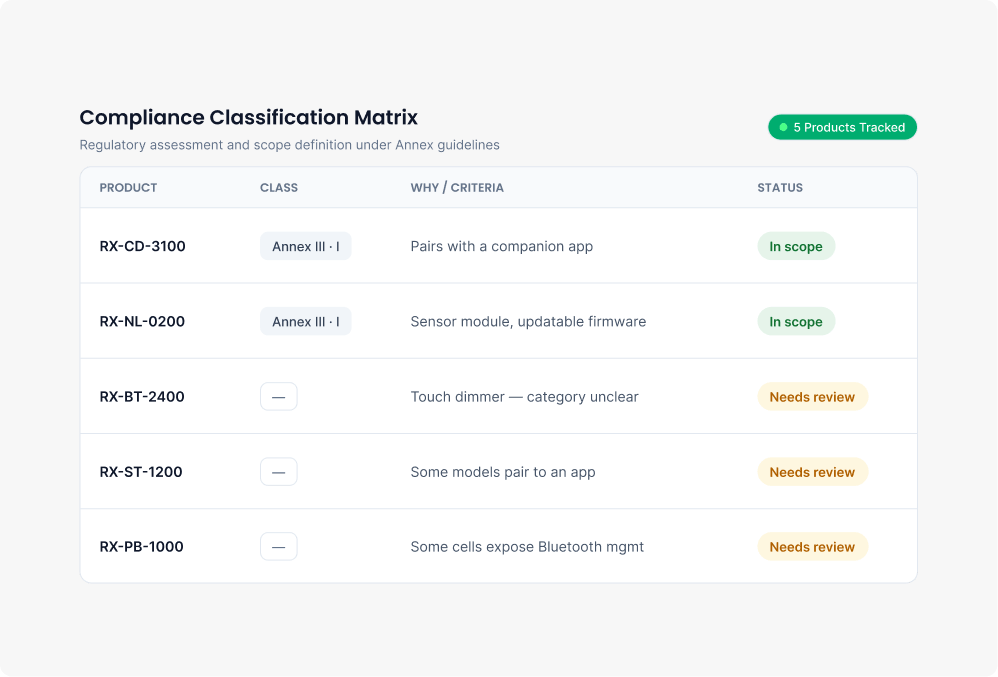
Screened from your catalogue, not from a questionnaire you have to fill in.
We classify every product on your Euverify account against the Regulation and tell you which fall inside it and at what risk class under Annex III or Annex IV. Where the category cannot settle it, we ask four short questions. You are not paying for representation on products that do not need it.
A readiness checklist you can actually finish
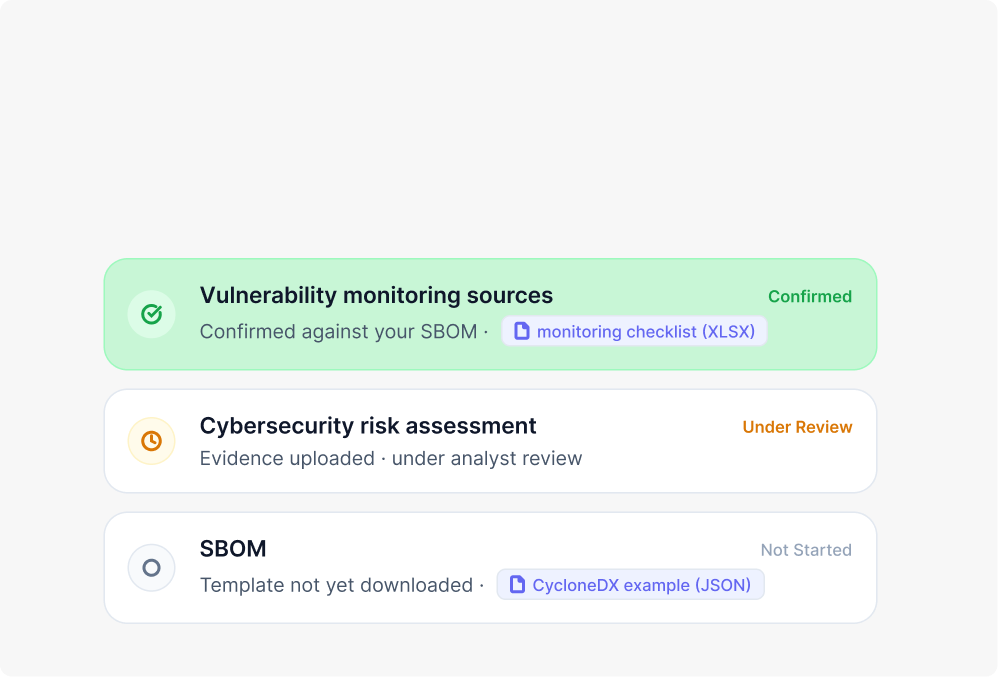
Templates, evidence upload, and a check by our analysts.
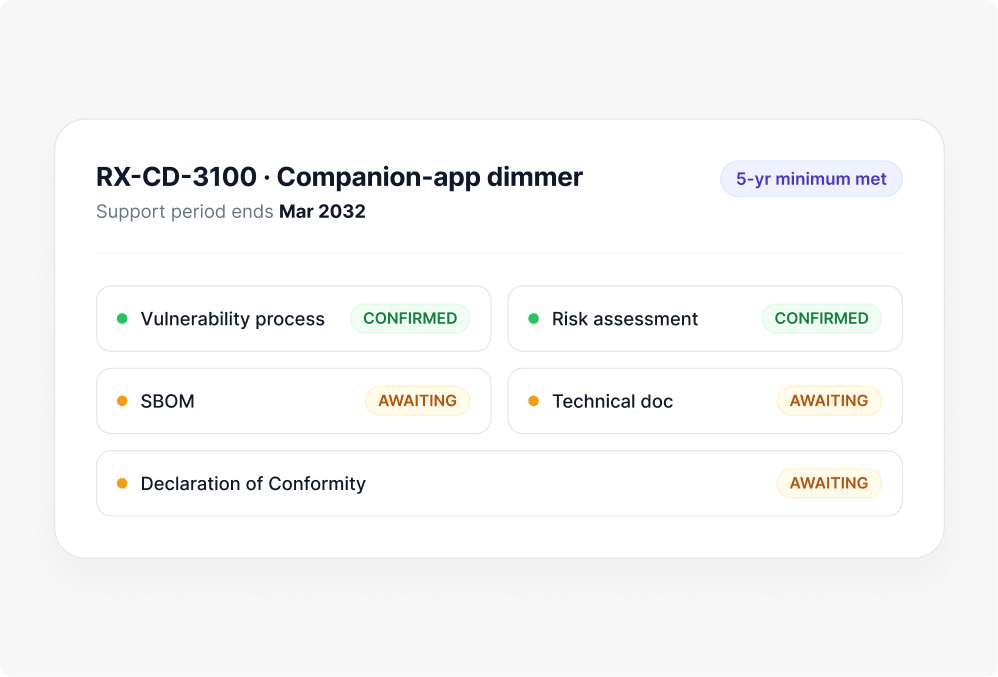
Point of contact, out-of-hours escalation, vulnerability handling process, coordinated disclosure policy, support period, SBOM. Download our template, fill it in, upload it. We confirm each item against what the Regulation asks for and mark it complete — so a tick on your dashboard means something to an authority.
Built for the December 2027 deadline, from today
Reporting first, documentation next.
Support period end dates with expiry alerts, SBOM storage, vulnerability and disclosure policy records, and an Annex VII documentation checklist per product — so by the time the full Regulation applies on 11 December 2027 there is nothing left to scramble for.
Key compliance steps
-
Sign the mandate
Euverify Limited (Ireland) becomes your authorised representative. Active the same day.
-
Exchange contacts
you give us a named escalation contact; we give you our out-of-hours route.
-
We screen your
catalogueevery product classified for CRA scope and risk class.
-
Complete the
readiness checklistdownload templates, upload evidence, we confirm each item.
-
If something
happensone call or one form starts the case; we work to the 24-hour clock.
-
Stay ahead of 2027
support periods tracked, documentation gaps reported before the deadline.
What this covers (and what it doesn’t)
Euverify CRA service does
- Act as your EU authorised representative under Article 18 by signed written mandate
- Hold your Declaration of Conformity and technical documentation for authorities, for 10 years or the support period, whichever is longer
- Answer reasoned requests from market surveillance authorities and cooperate on risk-elimination action
- Register as your Assigned Representative on the ENISA Single Reporting Platform
- Draft and submit your 24-hour early warning, 72-hour notification and final report, on your instructions
- Help draft the user notice required by Article 14(8)
- Screen your catalogue for CRA scope and Annex III / IV risk class
- Run the basic readiness checklist against your evidence and confirm each item
It does not (and here’s what to do instead)
- Take on your legal obligations. Article 18(2) puts product security, the risk assessment, the SBOM, the support period, security updates, the technical documentation and the legal duty to report outside any mandate. No representative can accept them, and any provider saying otherwise is describing something the Regulation does not permit.
- Detailed security assessment Risk assessments prepared for you, penetration testing, code review, SBOM generation and vulnerability programme design are specialist work. We introduce you to security partners who scope and price it directly with you — we don’t mark it up and we don’t take a fee from it.
- Decide whether an event is reportable. We help you think it through, but the call is yours. Our advice: if you’re unsure, report. Filing something that turns out not to be reportable costs you nothing.
- Conformity assessment or notified body work. Annex III Class I products need a notified body unless harmonised standards are fully applied; Class II always does. We tell you where you stand and who to go to.
- UK coverage.The CRA is EU law and there is no UK equivalent. Connected consumer products sold in Great Britain fall under the PSTI regime instead — ask us.
CRA deadlines have already started
-
Live Now 11 Sept 2026
Article 14 reporting: 24-hour early warning, 72-hour notification, final report. to products already on the market.
-
Approaching 11 Dec 2027
Full application: CE marking, EU Declaration of Conformity, technical documentation, conformity assessment, support period, SBOM, free security updates
-
Ongoing From 2027
Support period obligations run for at least five years per product, with security updates free for the whole period
Penalties reach €15 million or 2.5% of worldwide turnover.
If it connects and it has software, the CRA applies.
Medical devices under MDR and IVDR, motor vehicles, civil aviation and marine equipment are excluded – they have their own rules. So is anything with no connectivity and no software.
Already using Euverify for GPSR product safety?
We can tell you today which of your existing products fall under the CRA – we screen your catalogue
from the
records you already have. CRA representation is a separate mandate and a separate fee, because it is a
separate legal appointment.
-
Consumer electronics
smart TVs, speakers, wearables, cameras
-
Smart home and security
locks, doorbells, alarms, baby monitors (Annex III Class I)
-
Networking hardware
routers, modems, switches (Annex III Class I)
-
Health and fitness wearables
trackers, smartwatches, sleep monitors (Annex III Class I)
-
Connected toys
with a camera, microphone or location tracking (Annex III Class I)
-
Industrial and IoT
sensors, controllers, drones, EV chargers
-
Software and apps
where placed on the market separately, and companion apps a product needs to work
-
Non-EU brands with no EU presence
where the reporting route is decided for you unless you appoint a representative
Why Euverify
-
EU and UK registered
Euverify Limited in Ireland holds the Article 18 mandate; Euverify Ltd in London supplies the service. One relationship, both sides of the Channel. -
Reporting cover, not just a mailbox – an out-of-hours escalation route and one full notification cycle a year included, so the 24-hour deadline does not depend on office hours.
-
We say what we cannot do
Article 18(2) obligations stay with you, and we put that in writing before you sign rather than after something goes wrong. -
Written from the Regulation
our checks come from the text of Regulation (EU) 2024/2847 and ENISA’s platform guidance, not from summaries.

Book a Discovery Call
20 minutes with a compliance specialist. We look at your product range, tell you which items fall under the CRA and at what risk class, and show you exactly what the mandate does and does not cover.
Simple pricing, and you only pay for what a mandate actually is
CRA representation is a separate legal appointment, so it carries a separate fee.
CRA Representation
£590 / year
The Article 18 authorised representative service
- Euverify Limited (Ireland) named as your EU representative
- Declaration of Conformity and technical documentation held for authorities, 10 years or the support period
- We answer market surveillance authorities on your behalf
- EU point of contact for all authority correspondence
- Catalogue screened for CRA scope and Annex III / IV risk class
- Basic readiness checklist reviewed and confirmed
- Unlimited products covered by the mandate — no per-product fee
Reporting Cover
£390 / year
Managed reporting support
- Out-of-hours escalation route, so 24 hours does not depend on office hours
- Registered as your Assigned Representative on the ENISA Single Reporting Platform
- We draft and submit the 24-hour early warning, the 72-hour notification and the final report
- Help drafting the user notice required by Article 14(8)
- One notification cycle included each year — a cycle covers the initial notification, follow-up notification(s) and final report for the same reportable event
£980 a year for both
Additional notification cycles £1,500 each, fixed fee. Without Reporting Cover, emergency assistance is £2,500 per event on reasonable-endeavours terms with no deadline commitment.
All prices exclude VAT. VAT or any equivalent transaction tax is added only where it is properly chargeable, which depends on where your business is established.
Included at no extra cost
- Product scoping and risk classification
- Basic readiness checklist review of your evidence
- Every platform feature as it goes live — no upgrade fee
- Document custody after the agreement ends, for products already sold
- Adding products to your mandate as your range grows
- Introduction to a specialist security partner where a gap needs expert work
Requires a Euverify plan
CRA representation runs on top of a Euverify plan, because your product records live there. If you are already a Euverify customer, add CRA to your existing plan for £590.
If you are new, you will need a plan as well — see plans.
From £490/yrLoved & Trusted by Businesses Worldwide
Easy to use and excellent customer service if you need help with anything. If you’re wanting to sell on Amazon this makes everything easier, can’t recommend enough as saves me lots of time as a small business owner!.
The company goes above and beyond to provide great service and we look forward to working with them long term.
Friendly, efficient service; swift response to email. What’s not to like.
Trusted by 3,600+ verified brands
Frequently Asked Questions
Yes, in part. Reporting duties under Article 14 became live on 11 September 2026 and apply to products already on the market. The rest of the Regulation — CE marking, Declaration of Conformity, technical documentation, conformity assessment — applies from 11 December 2027.
For reporting, yes. If a vulnerability in something you sold in 2024 is being actively exploited today, the 24-hour duty applies. Products placed on the market before 11 December 2027 are otherwise exempt from the substantive requirements unless substantially modified.
No. Article 18 makes it voluntary, unlike GPSR. What it changes is practical: without one, Article 14(7) decides your reporting route by cascade — your importer, then your distributor, then wherever most of your users are. With one, it is fixed and predictable.
We hold your Declaration of Conformity and technical documentation for authorities for ten years or the support period, answer reasoned requests from market surveillance authorities, cooperate on risk-elimination action, and produce the mandate on request. With Reporting Cover we also draft and submit your Article 14 notifications.
Article 18(2) puts product security, the cybersecurity risk assessment, the SBOM, the support period, security updates, drawing up the technical documentation and the legal responsibility for reporting outside any mandate. Those stay with you and no representative can take them on.
A weakness in your product that someone is actually using against it, with evidence of real-world exploitation — not simply a flaw that exists. A flaw nobody is exploiting is not reportable under Article 14. You still fix it, but no 24-hour clock starts.
Something that has happened which affects the security of the product itself — for example an attacker reaching your build system and signing a malicious update. An outage, a bug, or a breach of your office email that does not touch product security is not a severe incident.
From the moment anyone in your organisation had enough information to reasonably conclude the vulnerability is being exploited or the incident has occurred. Not when the investigation finishes, and not when you tell us.
A CSIRT designated as coordinator and ENISA, at the same time, through the single reporting platform. All three stages — early warning, notification, final report — go to both.
Yes. Article 14(8) is a separate duty: you must inform impacted users about the vulnerability or incident and any mitigation they can apply. If you don’t do it in time, the notified CSIRT may do it for you. We help draft the notice; issuing it stays with you.
Products where the security stakes are higher: routers, modems and switches; smart locks, security cameras, baby monitors and alarms; health-monitoring wearables; connected toys with camera, microphone or location tracking; operating systems, browsers, password managers, VPNs and antivirus. Class I needs a notified body unless harmonised standards are applied in full; Class II always does.
No. The CRA is EU law and there is no UK equivalent. Connected consumer products sold in Great Britain fall under the PSTI regime instead.
£590 a year for the Article 18 representation service, and £390 a year for Reporting Cover, which includes one notification cycle. £980 for both, excluding VAT. It runs on top of a Euverify plan.
Because it is a separate legal appointment with a separate mandate and a standing on-call obligation, not a document module. PPWR conformity is something the platform generates; CRA representation is something a person is accountable for at 2am.
No, and we’re careful about that line. We confirm your documents and processes exist and cover what the Regulation asks for. Detailed assessment — risk assessments prepared for you, penetration testing, code review, SBOM generation — is specialist work, and we introduce you to security partners who price it directly with you.
Penalties under the CRA reach €15 million or 2.5% of worldwide turnover for breaches of the essential requirements and the Article 13 and 14 obligations. Market surveillance authorities can also require corrective action, restrict availability or withdraw a product from the market.
The 24-hour clock is already running
If a vulnerability in something you sold in 2024 is being actively exploited today, the duty applies now. Appoint us and you are represented the same day

Great 4.8 out of 5 based on 250 reviews